About
Hi, I’m JP.
I started KryptonBlue because small businesses get hit by the same threats as big companies, but they can’t afford the security teams big companies have. So I built the thing I wish my clients had: one person who actually knows your environment and answers when you call.
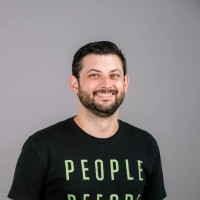
JP Russell
Founder, KryptonBlue
I’ve been in IT for 12 years. The first six I was a systems and network engineer, keeping small businesses and global enterprises running. The last six I’ve been in incident response and SOC work, the part of security where things are already on fire and you have to figure out why.
I’ve led incident response engagements and 0-day initiatives, and I’ve spent the last year or so looking at AI security. I found prompt-injection vulnerabilities in Microsoft Copilot: direct and indirect injection that led to system-prompt disclosure and file-upload bypasses. That work is why I’m confident I can spot the new stuff, not just the stuff that’s already in a signature database.
Outside of work I’m a husband and a dad of four, and I’m involved in a local homeless ministry. I take this job seriously because the people behind the accounts I protect are real.
Where the experience comes from
Over 12 years I’ve worked across a wide range of client environments, each with its own risks, compliance pressures, and ways of operating. That variety is what you get when you bring KryptonBlue in: someone who has already seen your kind of environment.
- Municipalities: public records and resident services running on aging infrastructure, with zero tolerance for downtime.
- Manufacturing: IT and OT sharing the same network, where a compromised workstation can reach the production floor.
- Utility Authorities: critical infrastructure under regulatory scrutiny, where uptime is non-negotiable.
- Healthcare: patient data and compliance obligations, with phishing that targets the front desk as much as the server room.
- Credit Unions: member data and financial systems where a single breach can be an existential event.
- Retail: card data, POS systems, and seasonal traffic spikes that stretch thin IT teams.
- Automotive: dealer management systems and inventory data spread across corporate and shop-floor networks.
Seeing the same environment from seven different angles is what sharpens the eye. When I review your network, I already know the mistakes your industry makes most, and I check for them first.
What I bring to the table
- 12 years in IT, 6 in incident response and SOC, before that systems and network engineering for SMBs and enterprises.
- Certifications: CEH, Security+, Network+. Currently studying for CPTS.
- Hands-on with the new threats, including finding prompt-injection flaws in Microsoft Copilot.
- Partner-backed tooling. I build on Sophos and SynchroMSP, so you get proven platforms managed by me. (Official partner badges coming once the partnerships are formalized.)
Who I help
Small and mid-sized businesses, roughly 10 to 500 people, that need real security but don’t want to hire a team. I’m based in the Austin area and work fully remote, so location isn’t a barrier.
Want to talk it through?
Tell me a bit about your business and I’ll tell you straight whether I’m the right fit, and what you should be doing about security either way.